ATTACK SURFACE RECON, THE WAY WORKING HUNTERS DO IT
Scan any domain. See every subdomain, technology, and known CVE — instantly.
NullBlocks is the attack surface recon engine hunters and consultants run against live targets — subdomain discovery, CVE correlation, dangling-subdomain takeovers, and bounty-coverage mapping, the first step, reconnaissance, in the Cyber Kill Chain.
Free report. No signup. Same tool, same output, whether you're learning or already working.
WHO IT'S FOR
One tool. Whether you're learning recon or you already do it for a living.
NullBlocks isn't a training sandbox you graduate out of. It's the reconnaissance engine security consultants and bounty hunters run against live targets — our Academy just teaches you how to use it well, so you walk away with a skill and a tool, not a certificate and a memory.
Working hunters and consultants
Skip the multi-tool passive recon pipeline. DomRecon handles subdomain enumeration, tech fingerprinting, and version-matched CVE correlation in one request — for any scope, in seconds.
Read the research →Learning bug bounty hunting
Start with the same recon engine you'll still be using a year from now. NullBlocks handles subdomain enumeration, tech fingerprinting, and version-matched CVE correlation, so the Academy can focus on teaching you to read the output and find the bug.
Learn on it →Breaking into security
No CTF background, no CS degree required to start. Attack-surface recon is the highest- leverage, most beginner-accessible skill in offensive security — and the tool you learn it on is the one practitioners already trust.
See a full footprint map →COMPARE
How NullBlocks stacks up.
NullBlocks vs Censys
An internet-wide search engine vs. a focused, correlated attack-surface report.
NullBlocks vs Pentest-Tools
A broad toolbox of individual scanners vs. one unified footprint report.
NullBlocks vs DIY Recon Stack
Building and maintaining your own pipeline vs. one tool that's already done that work.
The DomRecon Report
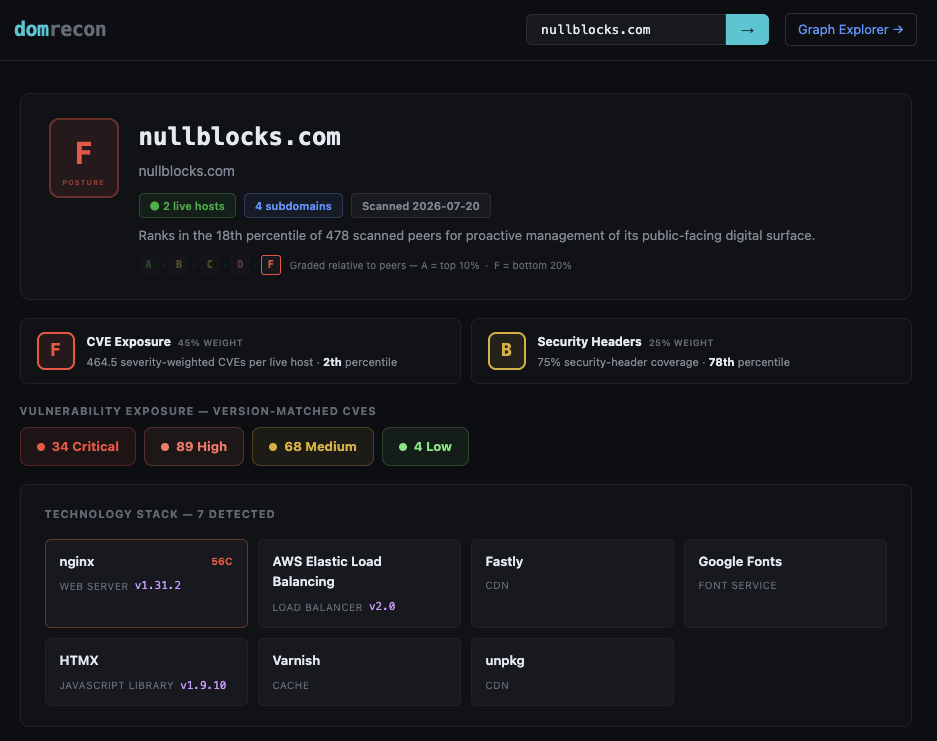
Type in any domain and get an instant snapshot of its attack surface: a clear risk grade, version-matched CVEs, the full technology stack, and a live list of subdomains. This is the production tool — the same report a consultant runs before a scope call.
- Plain-English risk grade, A through F
- Known CVEs matched to detected software versions
- Technology stack and live subdomain inventory
BEFORE YOU SCAN
Questions worth asking before you trust a tool with live targets.
Responsible-disclosure policy published. More third-party signals (Product Hunt, G2, press) will appear here as they're earned.
See the whole footprint, not just one report.
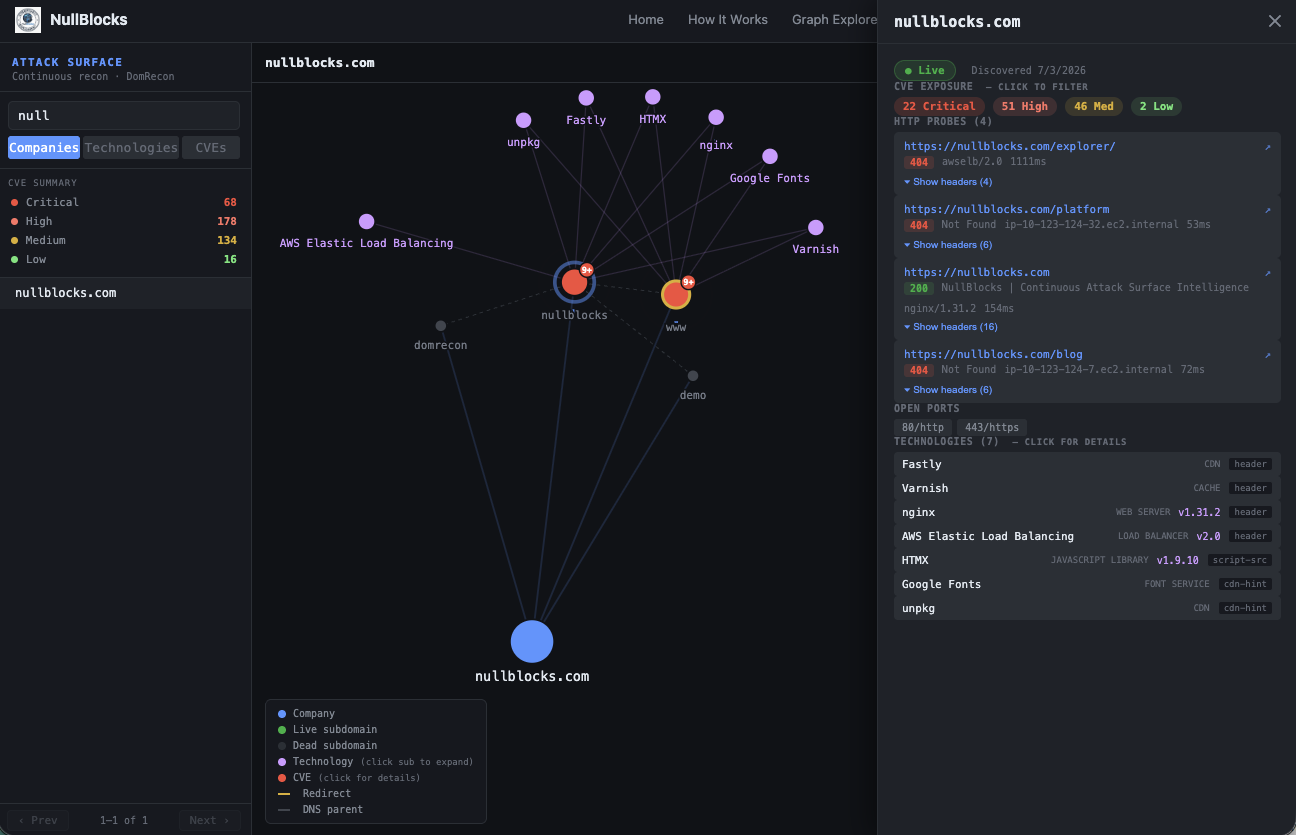
The free report is a single domain, once. Graph Explorer is every domain you own, mapped as a living graph and monitored continuously — every subdomain, host, technology, and CVE, with alerts when anything changes.
- Interactive footprint graph across your full portfolio
- Continuous rescans with a timestamped change log
- M&A and subsidiary mapping in one view
FOR SECURITY TEAMS
See what your organization exposes to the internet in plain English.
Continuous monitoring with change alerts means you hear about new exposure before an attacker does, not during an annual audit.
Want to learn recon from scratch instead?
The NullBlocks Academy teaches bug bounty hunting on this exact tool — real scans, real reports, from lesson one.
STAY AHEAD
Get free scan updates and research delivered to your inbox.
Leave your email and a domain you're curious about — we'll send you your first report, plus occasional research on real attack-surface exposure. No spam, no sales theatre — just useful signal.
Real humans read every reply. We typically respond within a day.